GitImage: a git URL in, a running pod out
A Kubernetes operator that builds every commit inside the cluster and rolls it out. No external CI, and with S3, no registry.
My homelab had one annoying routine. GitHub Actions built every project of mine into ghcr, and then every new version needed one more PR to the homelab repo, just to bump the image tag. One evening Hugin got two of those PRs in 13 minutes.
I wanted it simpler: push to git, and a minute later the new version is running. So two weeks ago I wrote GitImage, a Kubernetes operator that turns a git URL into a running pod.
How it works
You tell it where the repository is:
apiVersion: gitimage.dev/v1alpha1
kind: GitImage
metadata: { name: myapp, namespace: team-a }
spec:
  url: git@github.com:you/myapp.git
  ref: main
  secretRef: { name: myapp-git }
and put an annotation on a Deployment saying which container runs it. That's it.
Then on every commit GitImage:
- notices it, by watching the branch or through a webhook from GitHub, GitLab or Gitea;
- builds the image right inside the cluster with BuildKit;
- puts it into any registry or simply into an S3 bucket;
- rolls the Deployment out with the new image.
If a commit does not touch the image's code, nothing gets rebuilt: the last image is reused. And if a pod shows up before its image is ready, it just waits and starts as soon as the build is done.
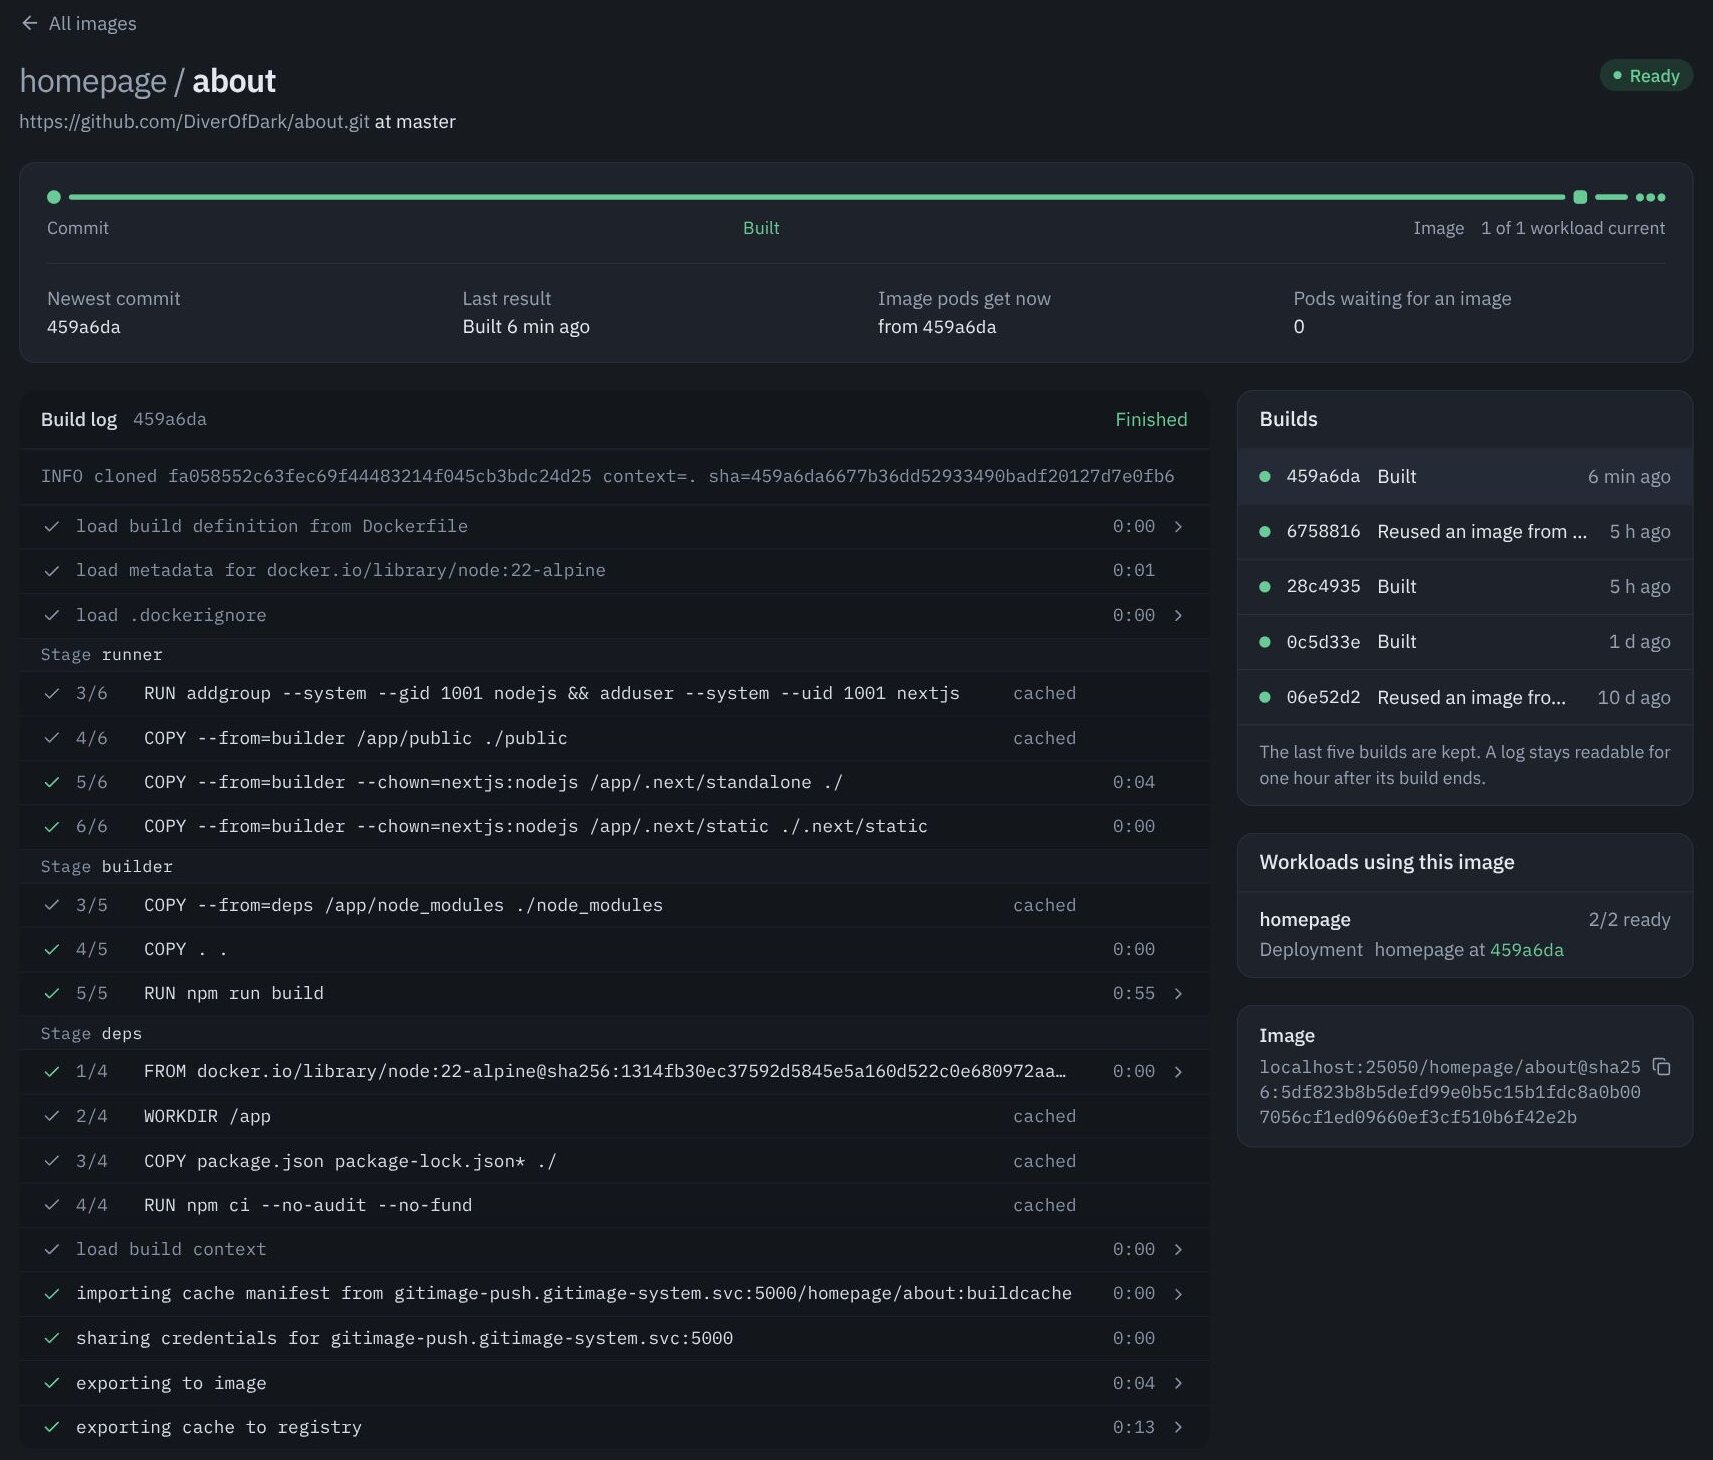
This is the page of this very blog, by the way 😅
The fun part: isolation
Building someone's Dockerfile in your cluster means running someone's code as root. So every build runs in its own sandbox: a separate VM with Kata, gVisor, Sysbox or user namespaces (all the modes). If the sandbox does not work, GitImage refuses to start at all.
At home this is where I spent the most time.
I started with Kata, and big builds kept dying: the VM ran out of memory. Two days later I gave up and moved to gVisor. It was even faster: crier built in about 3 minutes, while the first trackhound build under Kata had taken about 9.5.
Then I added phos, my photo manager, and gVisor just could not build it: apt broke while updating libssl. I tried a few workarounds. One crashed the sandbox, another one built phos in 57 minutes.
So after twelve days I went back to Kata, and this time dug down to the real cause. Kata gives the VM 2 GiB on top of the pod's memory limit, but the host only knew about the limit plus 130 MiB. As soon as the VM really used its memory, the host killed it. The whole fix was one number in the RuntimeClass: 130Mi became 2560Mi.
No registry needed
In S3 mode the images sit in a bucket (I use Ceph), and every node runs a tiny read-only server on localhost:25050 that containerd pulls from. So the whole "registry" is a bucket plus a DaemonSet.
The build never sees the bucket's keys, by the way. It pushes through GitImage with a token that works for this one image only and dies together with the build.
What is inside
- Rust, 8 crates: controller, admission webhook, node server and friends;
- gix for git, BuildKit for the builds;
- a web UI in Svelte with live build logs and login through OIDC;
- a Helm chart and docs.
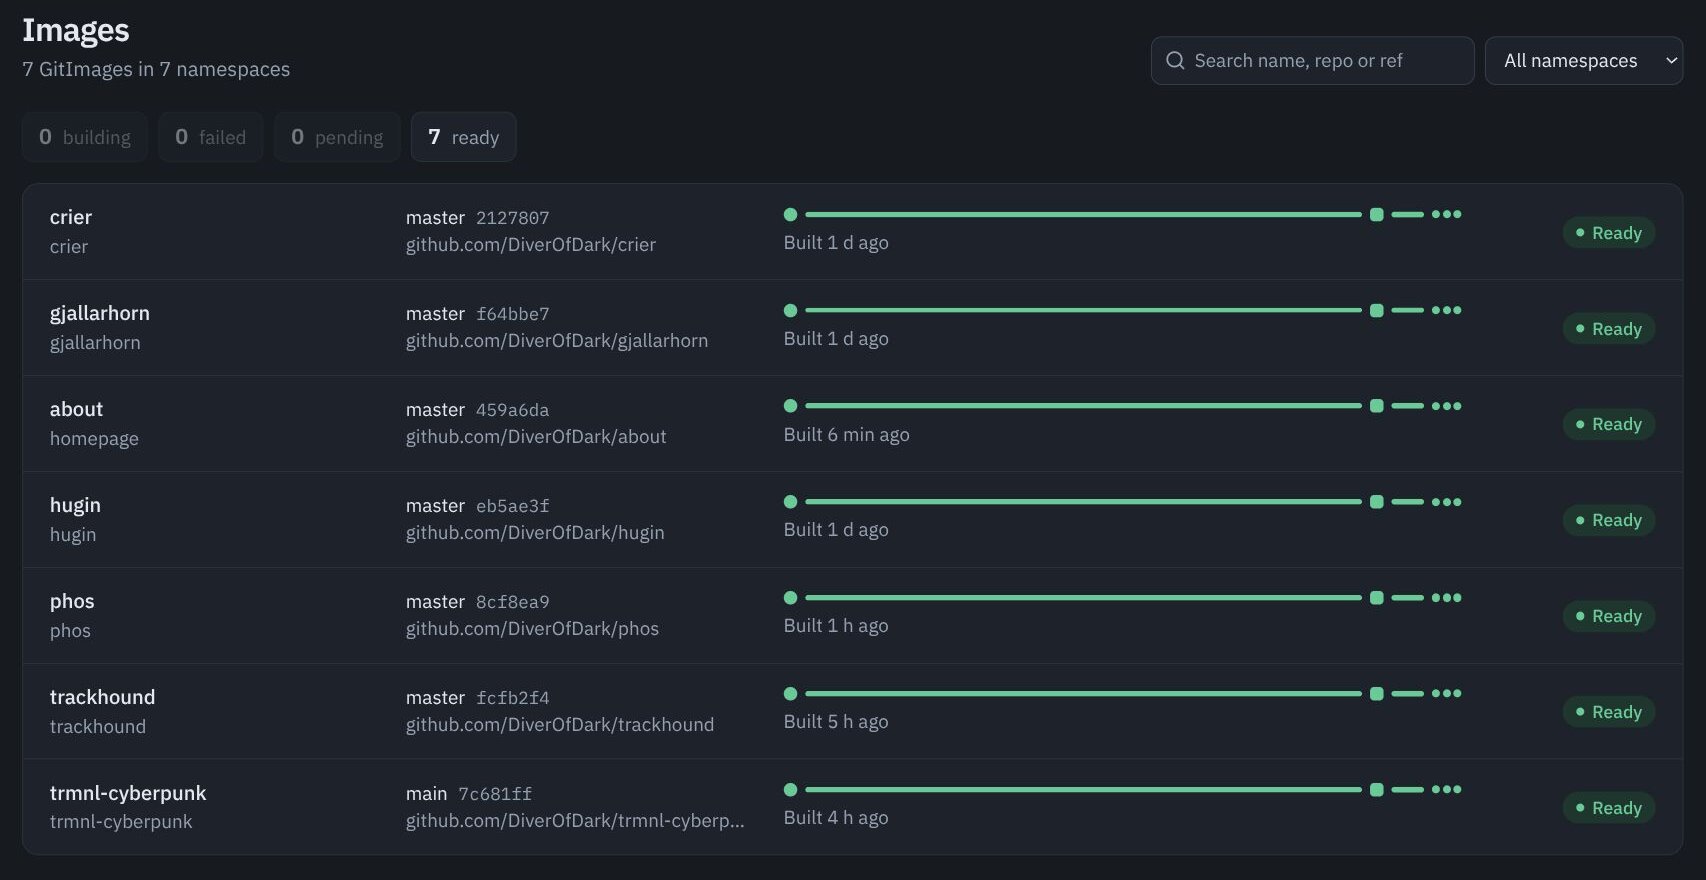
Right now it builds seven of my projects, this blog included, and I do not bump image tags by hand anymore. My setup is in the homelab repo.
It is pre-alpha: two weeks, 81 commits. It works for me, but I would not put it in production yet 😅 If you try it, I would be glad to hear how it went.